Special Halloween Sale - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 75vsure

350-701 Exam Dumps - Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)

Searching for workable clues to ace the Cisco 350-701 Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s 350-701 PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps

Go to page:
Question # 17

Which form of attack is launched using botnets?

A.

EIDDOS

B.

virus

C.

DDOS

D.

TCP flood

Full Access
Question # 18

An engineer must configure Cisco AMP for Endpoints so that it contains a list of files that should not be executed by users. These files must not be quarantined. Which action meets this configuration requirement?

A.

Identity the network IPs and place them in a blocked list.

B.

Modify the advanced custom detection list to include these files.

C.

Create an application control blocked applications list.

D.

Add a list for simple custom detection.

Full Access
Question # 19

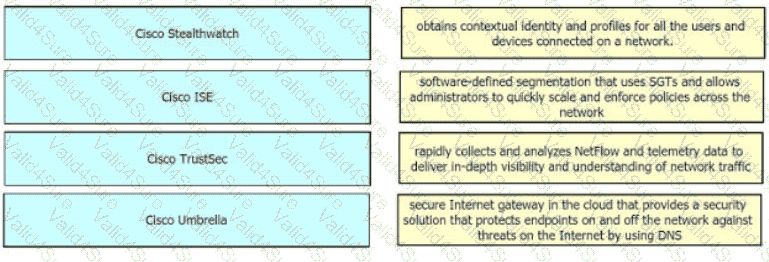
Drag and drop the solutions from the left onto the solution ' s benefits on the right.
Full Access
Question # 20

Which endpoint solution protects a user from a phishing attack?

A.

Cisco Identity Services Engine

B.

Cisco AnyConnect with ISE Posture module

C.

Cisco AnyConnect with Network Access Manager module

D.

Cisco AnyConnect with Umbrella Roaming Security module

Full Access
Question # 21

An organization recently installed a Cisco Secure Web Appliance and would like to take advantage of the AVC engine to allow the organization to create a policy to control application-specific activity. After enabling the AVC engine, what must be done to implement this?

A.

Use an access policy group to configure application control settings.

B.

Use security services to configure the traffic monitor.

C.

Use URL categorization to prevent the application traffic.

D.

Use web security reporting to validate engine functionality.

Full Access
Question # 22

For which two conditions can an endpoint be checked using ISE posture assessment? (Choose two)

A.

Windows service

B.

computer identity

C.

user identity

D.

Windows firewall

E.

default browser

Full Access
Question # 23

An administrator is adding a new Cisco ISE node to an existing deployment. What must be done to ensure that the addition of the node will be successful when inputting the FQDN?

A.

Change the IP address of the new Cisco ISE node to the same network as the others.

B.

Make the new Cisco ISE node a secondary PAN before registering it with the primary.

C.

Open port 8905 on the firewall between the Cisco ISE nodes

D.

Add the DNS entry for the new Cisco ISE node into the DNS server

Full Access
Question # 24

What is a feature of Cisco NetFlow Secure Event Logging for Cisco ASAs?

A.

Multiple NetFlow collectors are supported

B.

Advanced NetFlow v9 templates and legacy v5 formatting are supported

C.

Secure NetFlow connections are optimized for Cisco Prime Infrastructure

D.

Flow-create events are delayed

Full Access
Go to page: