SC-500 Exam Dumps - Microsoft Certified: Cloud and AI Security Engineer Associate
Searching for workable clues to ace the Microsoft SC-500 Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s SC-500 PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps
You have an Azure subscription named Sub1 that contains an Azure Database for PostgreSQL instance Sub1 has Microsoft Defender for Cloud enabled.
You need to configure Microsoft Defender for Databases to minimize costs.
Which Defender plan should you enable?
You have Microsoft Security Copilot agents that authenticate by using Microsoft Entra service principals.
You receive a Microsoft Defender alert triggered by the anomalous OAuth authentication of an agent ' s Microsoft Entra service principal.
You need to assess the impact of the agent identity and identify which resources are affected if the identity is abused for lateral movement The solution must minimize administrative effort.
What should you do?
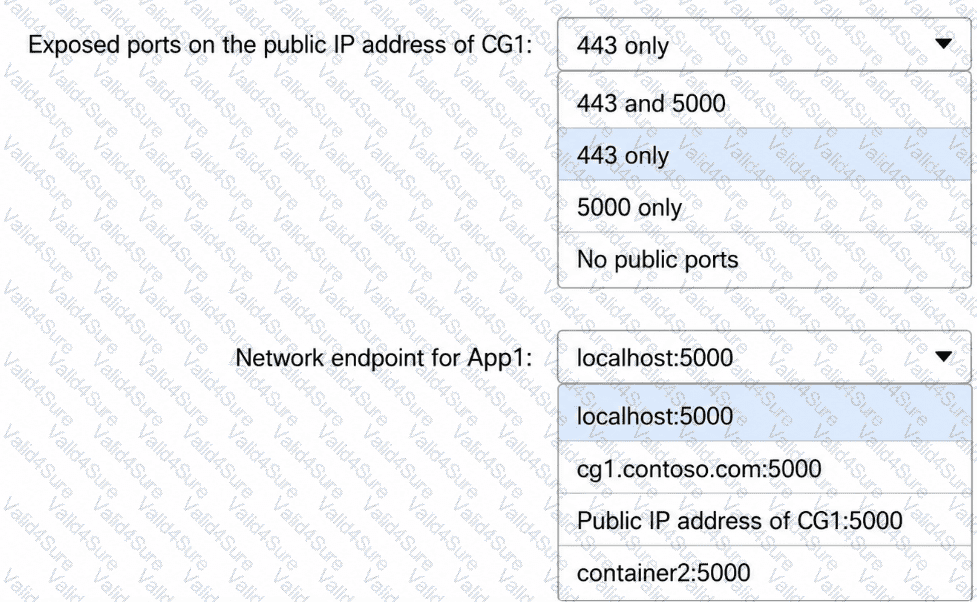
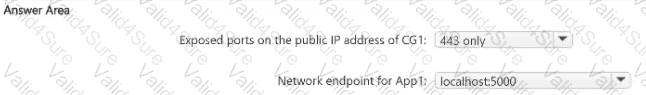
You have an Azure Container Instances container group named CG1 that has a DNS name of cg1.contoso.com. CG1 has the following configurations:
•A Linux container named container1 that serves HTTPS over TCP port 443 and hosts an application named App1
•A Linux container named container2 that listens on TCP port 5000 and is accessed only by App1
•A public IP address
A security review finds that external clients can reach TCP port 5000 by using the public IP address of CG1.
You need to meet the following requirements:
•Ensure that the external clients can access container1 only by using TCP port 443.
•Ensure that container1 can continue to access container2
What should you configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
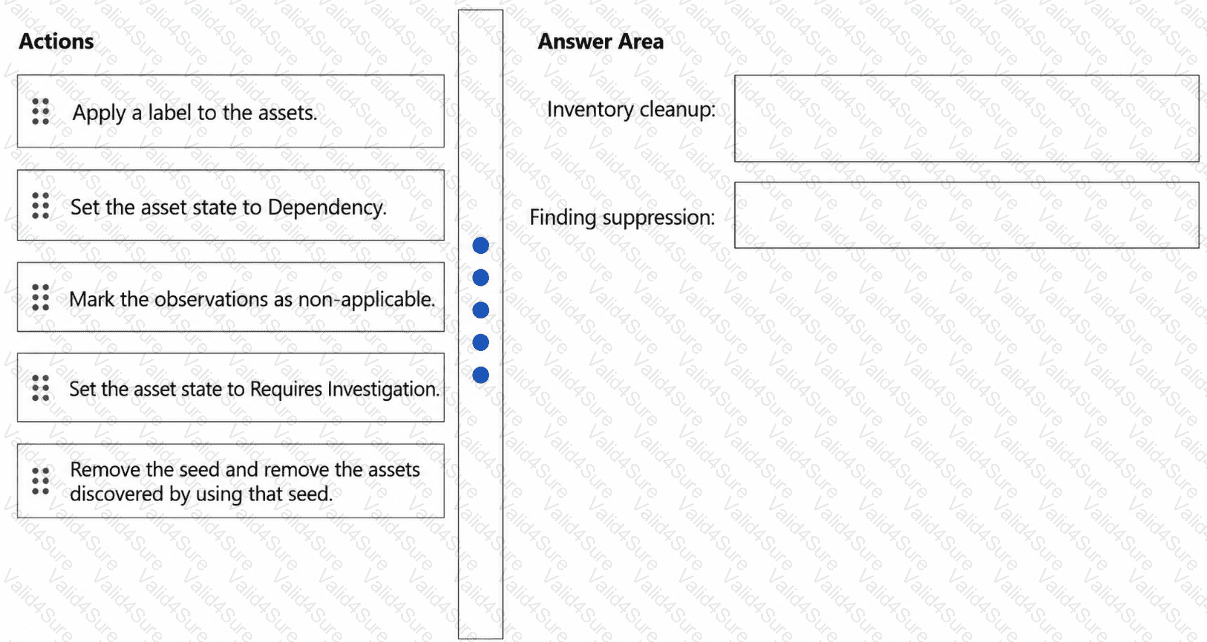
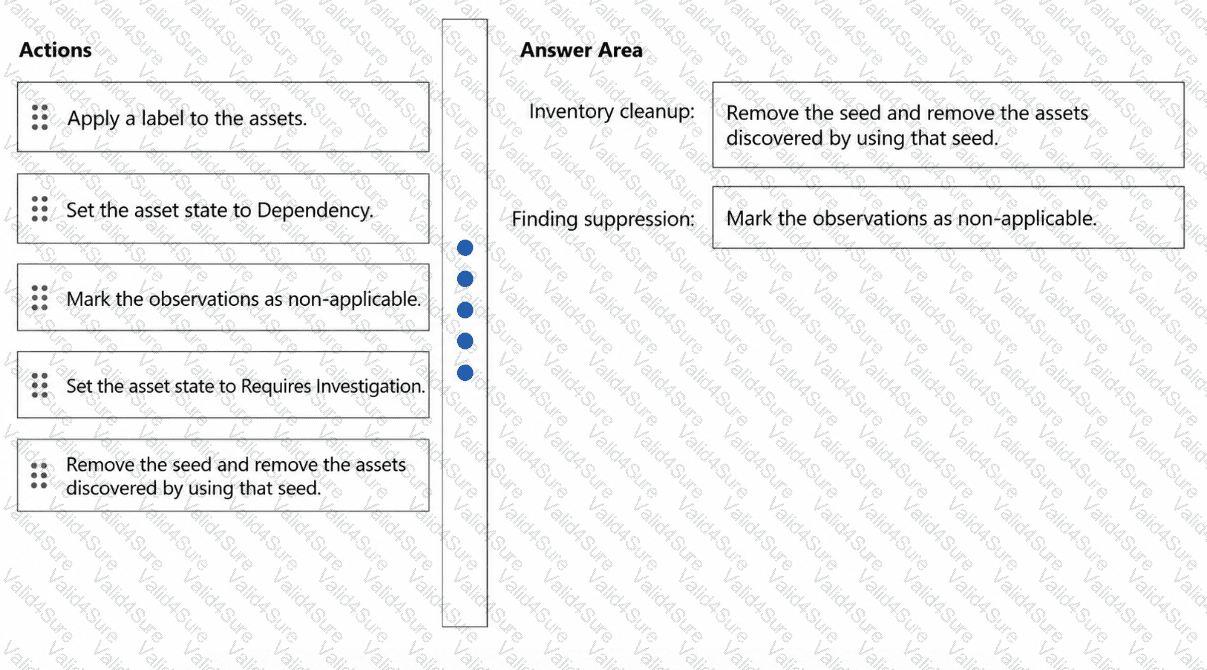
You have a Microsoft Defender External Attack Surface Management (Defender EASM) resource for a company named Contoso. Ltd.
You need to update the Defender EASM workflow to meet the following requirements:
•Assets from a business domain that Contoso no longer owns must be removed from inventory.
•Findings that do NOT apply to confirmed inventory must NOT affect reported counts.
What should you do for each requirement? To answer, drag the appropriate actions to the correct requirements. Each action may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You have a Microsoft Sentinel-enabled Log Analytics workspace named Workspace1.
Your company receives JSON security events from a software as a service (SaaS) application.
You plan to create a custom Microsoft Sentinel data connector.
You need to prepare Workspace1 for the incoming JSON data.
What should you do first?
You have the Azure key vaults shown in the following table.
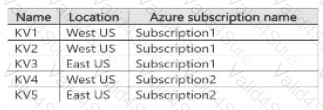
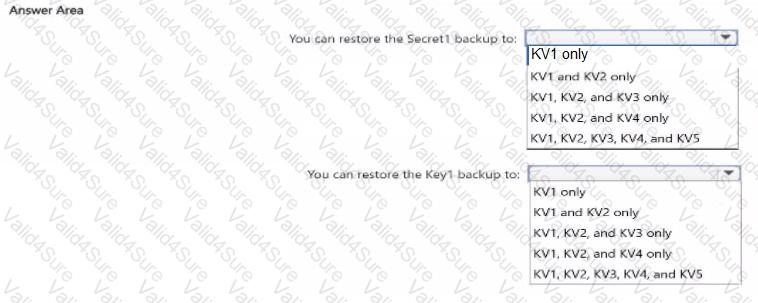
KV1 stores a secret named Secret1 and a key for a managed storage account named Key1.
You back up Secret1 and Key1.
To which key vaults can you restore each backup? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have 15 Azure virtual machines in a resource group named RG1.
All the virtual machines run identical applications.
You need to prevent unauthorized applications and malware from funning on the virtual machines. Authorized applications must be able to run on the virtual machines.
What should you do?
You have a Microsoft Entra tenant that contains a user named User1.
You have an Azure Arc-enabled server named SRV1 that runs Windows Server. SRV1 is configured for Microsoft Entra sign-in.
User1 reports that when they use their Microsoft Entra credentials to sign in to SRV1 over RDP, they receive the following message:
“Your account is configured to prevent you from using this device.â€
You need to ensure that User1 can sign in to SRV1 over RDP. The solution must follow the principle of least privilege.
What should you do?