SC-500 Exam Dumps - Microsoft Certified: Cloud and AI Security Engineer Associate
Searching for workable clues to ace the Microsoft SC-500 Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s SC-500 PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps
You have an Azure subscription named Sub1 that contains multiple virtual machines and an Azure key vault named KV1.
Each virtual machine has a system-assigned managed identity. Sub1 has Microsoft Defender for Servers enabled. Defender for Servers has agentless scanning enabled.
Some virtual machines use managed disks that are encrypted by using customer-managed keys stored in KV1.
You discover that the affected virtual machines fail to return agentless scanning results in Microsoft Defender for Cloud.
You need to ensure that agentless scanning can analyze the virtual machines.
What should you do?
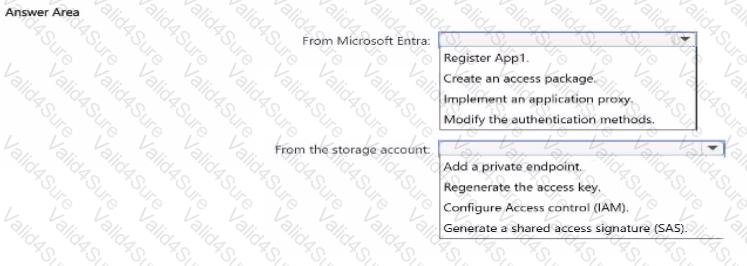
You have an Azure Storage account that contains a blob container named container 1 and a client application named App1. You need to enable App1 access to container1 by using Microsoft Entra authentication. What should you do ' To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have a Microsoft Entra tenant that has user consent for applications disabled.
You register an application named App1 that requests the following Microsoft Graph delegated permissions:
•user.Read
•Mail.Read
You need to configure tenant permissions to meet the following requirements:
•Enable users to grant consent for low-risk permissions without administrator interaction.
•Ensure that applications requesting higher-privilege permissions require administrator approval.
What should you do?
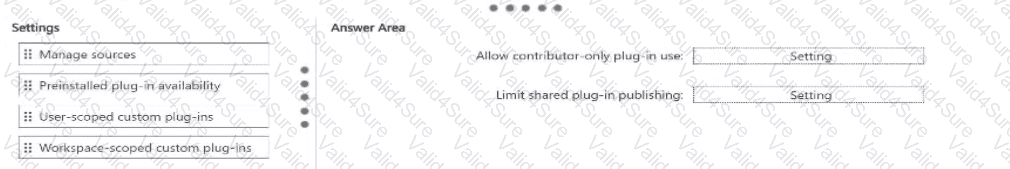
You use Microsoft Security Copilot.
You need to update Plugin settings. the solution must meet the following requirements:
• Allow contributors to use custom plug-ins without affecting either UMTS
• Limit publishing of custom plug-ins for other users to Owners only.
Which Plugin settings option should you configure for each requirement? To answer, drag the appropriate settings lo the correct requirements. Each setting may be used once, more than once., or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You have a Microsoft Entra tenant that has the following configurations:
•User consent for applications is disabled.
•Only administrators can grant permissions to applications.
You register an application named App1 that uses delegated Microsoft Graph permissions.
You need to configure App1 to meet the following requirements:
•Enable user sign-ins without interactive consent prompts.
•Enable App1 to access Microsoft Graph on behalf of the signed-in user.
What should you do?
You have an Azure subscription that contains an Azure SQL Database logical server named SQL1 and an Azure virtual machine named VM1. VM1 uses a private IP address only. The Firewall and virtual networks settings for SQL1 are shown in the following exhibit.
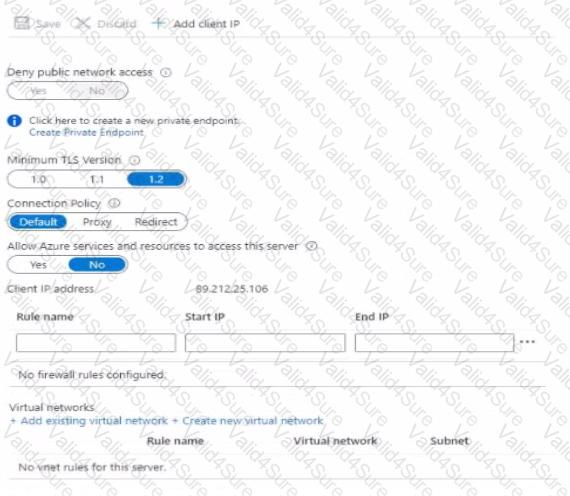
You need to ensure that VM1 can connect to SQL1. The solution must use the principle of least privilege.
What should you do on the SQL1 Firewall and virtual network settings?
You have an Azure SQL Database logical server named Server1 that contains a database named DB1.
You need to configure authentication for Server1 to meet the following requirements;
•SQL authentication cannot be used for any databases on Server1.
•The solution must be enforced centrally at the server level.
What should you do?
You have an Azure virtual network named VNet1 that contains a subnet named Subnet! A network security group named NSG1 is associated with Subnet1.
Vou have a storage account named storage1.
You need to ensure that access from Subnet1 to storage! uses a private IP address in Subnet1 and ran be filtered by NSG1 Public network access to storage1 must be disabled.
What should you create?