SC-500 Exam Dumps - Microsoft Certified: Cloud and AI Security Engineer Associate
Searching for workable clues to ace the Microsoft SC-500 Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s SC-500 PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps
You have a Microsoft Entra tenant that contains the users shown in the following table.
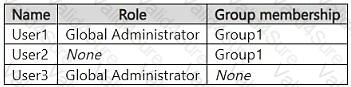
The tenant contains a Conditional Access policy named CA1 that has the following settings:
Assignments:
o Users or agents:
- Include: Directory roles: Global Administrator
Target resources:
o Resources (formerly cloud apps):
- Include: All resources
Conditions:
o Locations:
- Configure: Yes
- Include: Any network or location
Access controls:
o Grant:
- Require multifactor authentication
o Grant:
- Require device to be marked as compliant
o For multiple controls:
- Require all the selected controls
The tenant contains a Conditional Access policy named CA2 that has the following settings:
Assignments:
o Users or agents:
- Include: Users and groups: Group1
Target resources:
o Resources (formerly cloud apps)
- Include: Select resources: Office 365
Conditions:
o Locations:
- Configure: Yes
- Include: Any network or location
Access controls:
o Grant:
- Require multifactor authentication
o Grant:
- Require app protection policy
o For multiple controls:
- Require one of the selected controls
The users perform the following tasks:
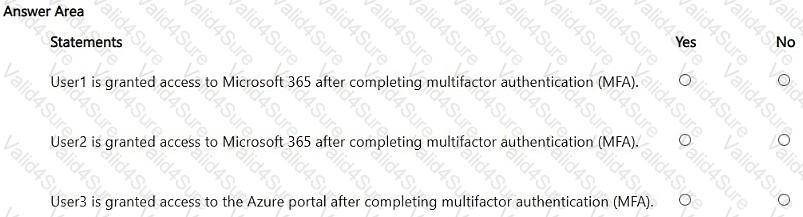
User1 signs in to Microsoft 365 from a home network by using Microsoft Outlook on a noncompliant device.
User2 signs in to Microsoft 365 without an app protection policy by using a noncompliant device.
User3 signs in to the Azure portal from a home network by using a compliant device.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
You have an Azure management group named MG1 that contains two subscriptions named Sub1 and Sub? Both subscriptions are linked to a Microsoft Entra tenant that contains a security group named Group!
You need to ensure that the members of Group1 can assign roles to the resources in Sub1 and Sub2. The solution must follow the principle of least privilege.
Which role should you assign to Group1?
You have a Microsoft 365 subscription.
You use Microsoft Entra Agent ID to manage an agent identity.
You manage AI agents from the Microsoft 365 admin center.
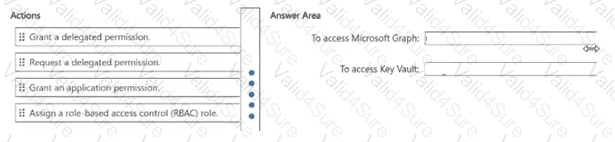
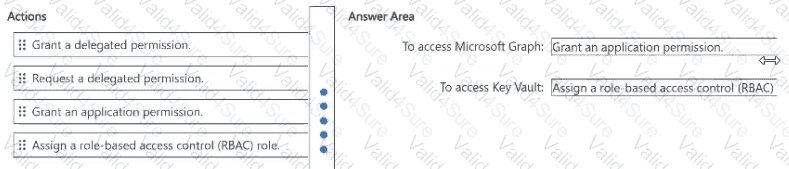
An autonomous agent named Agent1 runs without a signed-in user. The agent must access Microsoft Graph and read secrets from a single Azure key vault.
You need to grant Agent 1 access to Microsoft Graph and Key Vault without requiring user interaction or consent at runtime.
What should you do for the agent identity? To answer, drag the appropriate actions to the correct services. Each action may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You have a Microsoft Entra tenant that contains a group named Group1.
You plan to target Group1 to use the Microsoft Authenticator authentication method.
You need to ensure that the members in Group1 can use the Authenticator app as their primary authentication method.
What should you do?
You have an Azure subscription that contains the resources shown in the following table.
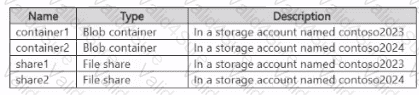
You create a shared access token as shown in the following exhibit.
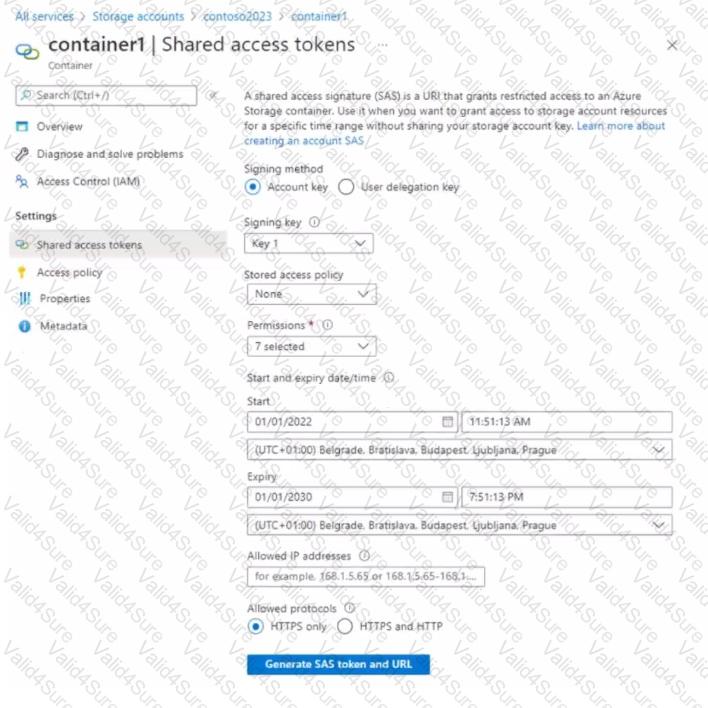
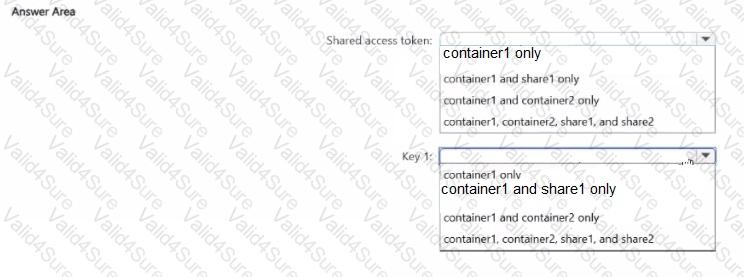
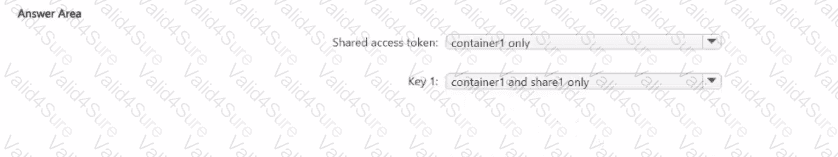
Which resources can you access by using the shared access token and Key 1? To answer, select the appropriate options in the answer area.
NOTE: Each correct answer is worth one point.
You need to implement the planned change for VM1 to access storage1. The solution must meet the technical requirements.
What should you do first?
You have an Azure subscription.
You need to deploy an Azure virtual WAN to meet the following requirements:
•Create three secured virtual hubs located in the East US. West US, and North Europe Azure regions.
•Ensure that security rules sync between the regions.
What should you use?
You have an Azure Container Registry named Registry1-
You add role assignments for Registry1 as shown in the following table.