NSE5_FWB_AD-8.0 Exam Dumps - Fortinet NSE 5 - FortiWeb 8.0 Administrator
Searching for workable clues to ace the Fortinet NSE5_FWB_AD-8.0 Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s NSE5_FWB_AD-8.0 PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps
Refer to the exhibit.
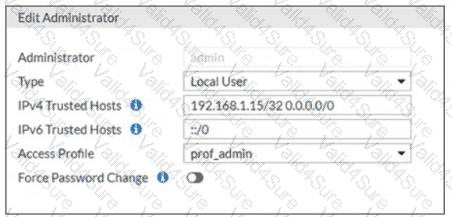
There is only one administrator account configured on FortiWeb and IPv6 is not configured on any interface.
Which action should an administrator take to restrict any brute force attacks that attempt to gain access to the FortiWeb management GUI?
A FortiWeb administrator wants to stop coordinated scraping traffic coming from several IP addresses, each making only a few requests so thresholds never trigger.
Which tactic should the administrator deploy to identify botnets using shared behavioral signals instead of volume?