
HPE7-A10 Exam Dumps - HPE Network Security Expert Written Exam
Searching for workable clues to ace the HP HPE7-A10 Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s HPE7-A10 PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps
Introduction to the customer
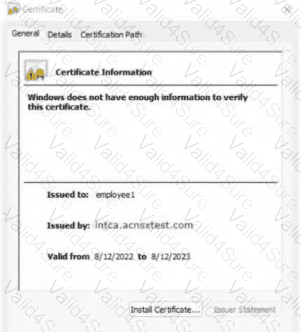
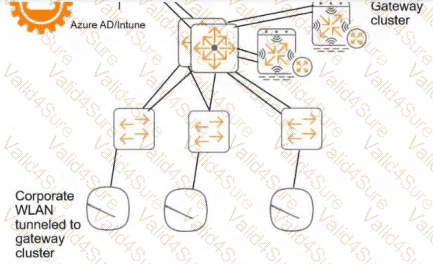
You are assisting a company with adding HPE Aruba Networking ClearPass to its network, which uses HPE Aruba Networking network-infrastructure devices.
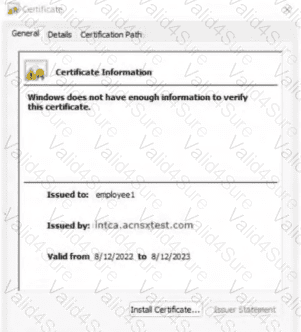
The company already has a Windows domain and Windows CA. The Windows CA issues certificates to domain computers, domain users, and servers such as domain controllers.
ClearPass cluster IP addressing and hostnames
Publisher = 10.47.47.5
Subscriber 1 = 10.47.47.6
Subscriber 2 = 10.47.47.7
Virtual IP with Subscriber 1 and Subscriber 2 = 10.47.47.8
Refer to the scenario.
You imported the root certificate for the Windows CA into the ClearPass CA Trust list. Based on the scenario requirements, which usages should be added to it?
A customer uses an AOS-10 architecture that includes HPE Aruba Networking APs. Administrators recently enabled WIDS at the High level and also enabled alerts and email notifications for several events.
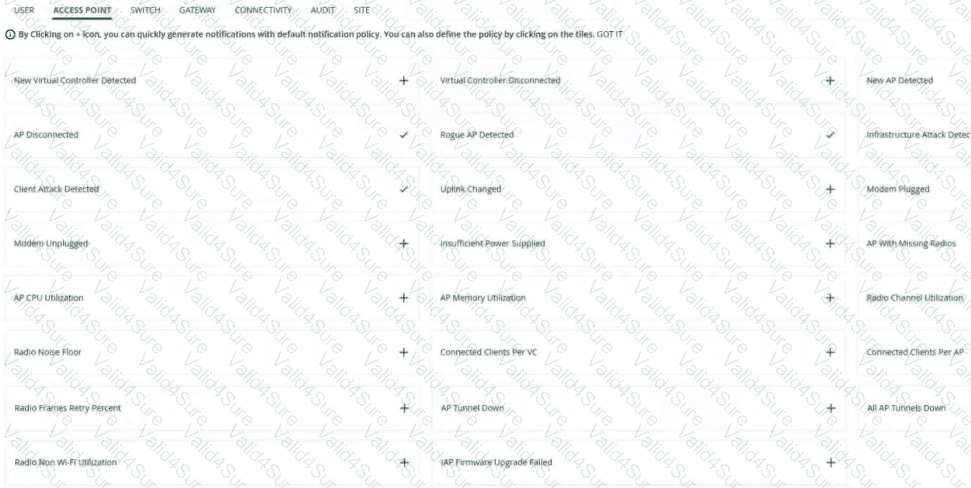
Administrators report receiving so many emails that they must ignore them and are considering disabling all notifications. What is one step you could recommend trying first?
How does HPE Aruba Networking Central secure site-to-site connections between AOS-10 gateways?
Introduction to the customer
You are assisting a company with adding HPE Aruba Networking ClearPass to its network, which uses HPE Aruba Networking infrastructure devices.
The company already has a Windows domain and Windows CA. The Windows CA issues certificates to domain computers, domain users, and servers such as domain controllers.
ClearPass cluster IP addressing and hostnames
A customer's ClearPass cluster uses these IP addresses:
Publisher = 10.47.47.5
Subscriber 1 = 10.47.47.6
Subscriber 2 = 10.47.47.7
Virtual IP with Subscriber 1 and Subscriber 2 = 10.47.47.8
The customer's DNS server contains these entries:
cp.acnsxtest.com = 10.47.47.5
cps1.acnsxtest.com = 10.47.47.6
cps2.acnsxtest.com = 10.47.47.7
radius.acnsxtest.com = 10.47.47.8
onboard.acnsxtest.com = 10.47.47.8
Refer to the scenario.
The Onboard CA uses the settings shown in the exhibits below.
* CA Name: Onboard CA, CA ID: 2
* Common Name: ClearPass Intune Certificate Authority
Microsoft Entra ID (Azure AD) administrators need assistance configuring the app registration for integration with ClearPass Onboard.
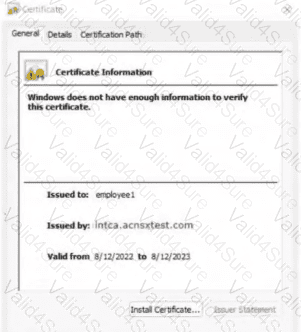
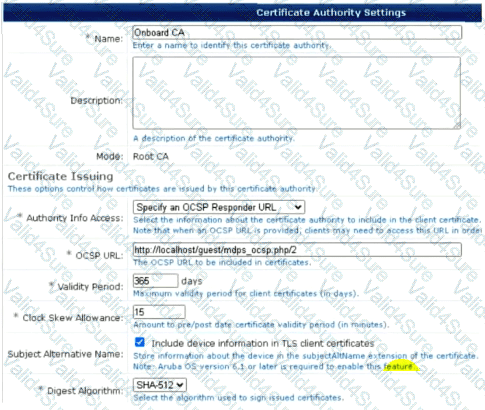
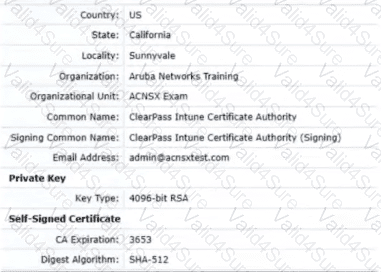
Which URL should you tell them to use?
Refer to the scenario.
A customer has AOS-CX switches with this configuration on their edge ports:
port-access onboarding-method concurrent enable
aaa authentication port-access mac-auth enable
quiet-period 60
aaa authentication port-access dot1x authenticator enable
The switch authenticates clients to HPE Aruba Networking ClearPass Policy Manager (CPPM), which has these services:
An 802.1X service that uses an EAP-TLS method for most clients
A MAC-Auth service that uses the [MAC-Auth] method for devices such as printers imported from an inventory manager
The customer now wants to give limited access to wired guest devices and new devices that must be enrolled with certificates. You have configured these rights in an AOS-CX role named "guest-login."
How should the "guest-login" role be applied on the switches?
What benefit does an organization obtain by upgrading wireless security from WPA2-Personal to WPA3-Personal?
A customer operates an HPE Aruba Networking ClearPass cluster. The customer has AOS-CX switches that use 802.1X authentication with HPE Aruba Networking ClearPass Policy Manager (CPPM).
The switches use local port-access policies. The customer wants to begin tunneling wired clients that pass only user authentication to an HPE Aruba Networking gateway cluster. The gateway cluster must assign these clients the eth-internet role. The gateway must also assign the clients to VLAN 20.
The intended enforcement policy and profiles are shown below:
* Policy: `written-exam-3`
* Profile: `written-exam-b`
The gateway cluster contains two gateways with the following IP addresses:
Gateway 1: VLAN 4085 (system IP) = 10.20.4.21 | VLAN 20 (users) = 10.20.20.1 | VLAN 4094 (WAN) = 198.51.100.14
Gateway 2: VLAN 4085 (system IP) = 10.20.4.22 | VLAN 20 (users) = 10.20.20.2 | VLAN 4094 (WAN) = 198.51.100.12 | VRRP on VLAN 20 = 10.20.20.254
The customer needs high availability for tunnels between the switches and the gateway cluster. If one gateway fails, the other gateway must take over its tunnels. The switch must also be able to discover the gateway cluster even if one gateway in the cluster is unavailable.
Refer to the scenario. Assume that `myzone` is the name used for the UBT zone.
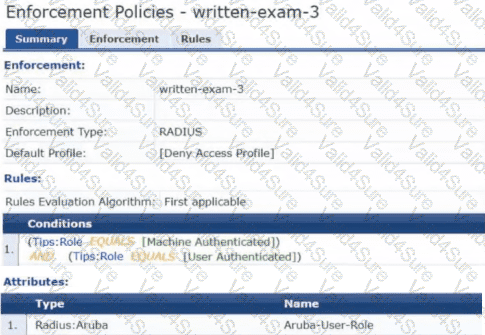
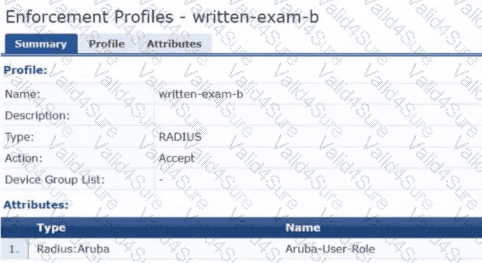
Which option is a valid minimal configuration for the AOS-CX port-access roles?
A customer uses an AOS-10 architecture that includes HPE Aruba Networking APs. The customer recently enabled WIDS at the High level on the APs. Administrators observe many "detect disconnect station" events.
What should you explain?