
Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: scxmas70

CCAR-P Exam Dumps - Claude Certified Architect - Professional

Searching for workable clues to ace the Anthropic CCAR-P Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s CCAR-P PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps

Go to page:
Question # 17

You are compiling team-setup practices for a Claude Code rollout across an engineering organization.

Which two practices belong on the list? (Select two.)

Each correct answer presents a complete solution.

A.

Use project scope for team-shared Model Context Protocol (MCP) servers and permission rules under version control.

B.

Apply managed configuration centrally for security-critical settings that must not be overridden by individual engineers.

C.

Use local scope for security-critical permission rules so each engineer can adapt them to ongoing work.

D.

Use user scope for team-shared MCP servers so every engineer on the team has consistent access.

E.

Use project scope for personal editor preferences so the preferences apply consistently within the project.

Full Access
Question # 18

An engineer inadvertently commits an API key to the repository by placing it in .claude/settings.json.

Which configuration design principle was violated?

A.

Project-scope configuration should always override user-scope configuration.

B.

Managed configuration must be applied before project-scope configuration is read.

C.

Credentials must be resolved at runtime from a secret store and never stored in version-controlled files.

D.

MCP server definitions must reside in environment variables to prevent scope conflicts.

Full Access
Question # 19

You are defining transparency practices for a customer-facing assistant whose responses are materially shaped by AI.

Which transparency practice most directly supports responsible deployment?

A.

Misrepresent the AI’s role in producing responses in order to make the assistant feel more trustworthy or more human, undermining informed user consent and organizational transparency.

B.

Refuse to answer any user question about how the responses were produced or whether AI was involved, treating the AI’s role as confidential operational information.

C.

Disclose AI involvement to end users in line with the organization’s transparency policy and provide a documented path to reach a human when needed.

D.

Disclose AI involvement only to internal staff and operators while withholding that information from the end users whose interactions are materially shaped by the AI system.

Full Access
Question # 20

You are supporting an engineer whose Claude Code session reports a permission denial when the engineer expected the action to be allowed.

Which resolution step is most appropriate?

A.

Tell the engineer to retry the denied action verbatim repeatedly until the denial stops appearing, without inspecting the active permission rules to determine whether the denial is intentional.

B.

Disable the permission system entirely across all scopes to remove the denial, eliminating all tool-pattern and deny-rule controls rather than identifying and amending the specific rule.

C.

Inspect the active permission rules across all scopes—managed, command-line, local, project, and user—to identify which rule is denying the action and confirm whether it should be amended or remain denied.

D.

Grant the engineer unrestricted Bash access to bypass the specific rule causing the denial, removing all tool-pattern constraints rather than amending only the rule in question.

Full Access
Question # 21

A pilot AI assistant for procurement specialists shows 89 percent first-response acceptance, but follow-up surveys reveal that specialists frequently override the assistant’s vendor recommendations after considering criteria the assistant did not evaluate. The pilot owner wants to ship the assistant unchanged because of the strong acceptance rate.

Which two Discernment-competency observations should you raise BEFORE approving the launch? (Select two.)

A.

The acceptance rate alone proves readiness for general production use.

B.

The survey response rate may not be statistically representative of all specialists.

C.

The unconsidered criteria represent a scope gap in the assistant’s input space.

D.

Acceptance does not establish whether recommendations remain correct after specialist review.

E.

The pilot duration was probably too short to demonstrate reliability across the full year.

Full Access
Question # 22

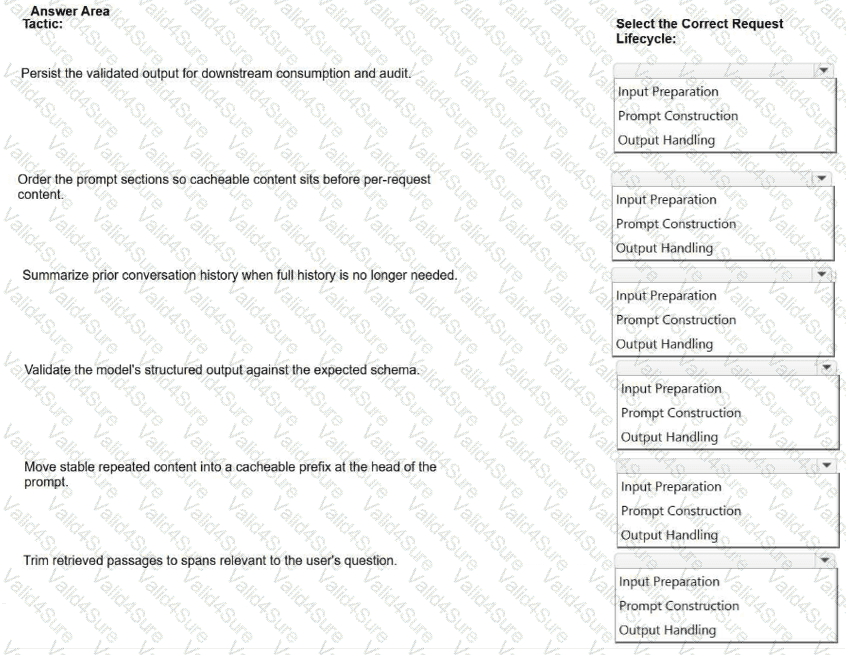
You are classifying token-management tactics by where in the request lifecycle each tactic applies.

For each tactic, select where in the request lifecycle it applies: Input Preparation , Prompt Construction , or Output Handling .
Full Access
Question # 23

You are selecting the documentation set that should accompany a Claude-based deployment at handoff. Which set is most complete?

A.

Architecture overview, ADRs, component-level diagrams, runbooks for common operations, an on-call playbook, and a list of known limitations.

B.

Code comments scattered across individual source files with no integrating architecture overview, no ADRs, no runbooks, and no on-call playbook to orient operators or new team members.

C.

A single one-page architecture diagram with no ADRs, no runbooks, no on-call playbook, and no list of known limitations to support operators or future maintainers.

D.

A verbal handover walkthrough conducted on the day of transition, with no written architecture overview, ADRs, runbooks, playbook, or known limitations captured for future reference.

Full Access
Question # 24

During an architectural review, the security team identifies a risk that adversarial content injected into retrieved documents could manipulate the model’s behavior.

Which mitigation most directly addresses this threat?

A.

Treat all retrieved content as untrusted input and apply input classifiers with output validation.

B.

Require citations for each claim and constrain responses to source-supported content.

C.

Restrict outbound tool calls to an approved destination allow-list.

D.

Score outputs against a stable adversarial evaluation set on each model-version change.

Full Access
Go to page: