Special Halloween Sale - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 75vsure

350-701 Exam Dumps - Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)

Searching for workable clues to ace the Cisco 350-701 Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s 350-701 PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps

Go to page:
Question # 121

What is the most common type of data exfiltration that organizations currently experience?
A.

HTTPS file upload site

B.

Microsoft Windows network shares

C.

SQL database injections

D.

encrypted SMTP

Full Access
Question # 122

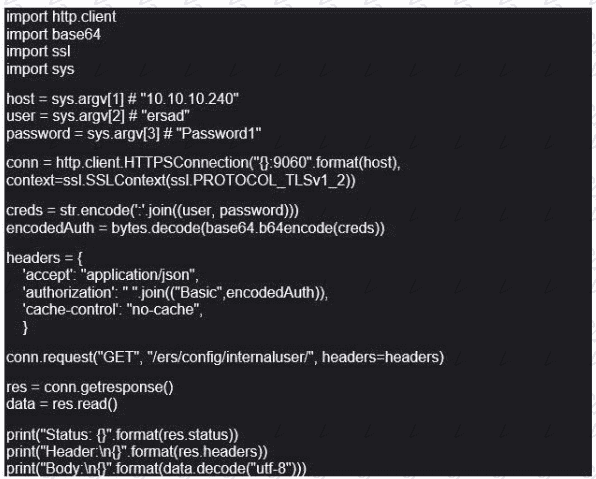
Refer to the exhibit. What does this Python script accomplish?

A.

It allows authentication with TLSv1 SSL protocol

B.

It authenticates to a Cisco ISE with an SSH connection.

C.

lt authenticates to a Cisco ISE server using the username of ersad

D.

It lists the LDAP users from the external identity store configured on Cisco ISE

Full Access
Question # 123

A company has 5000 Windows users on its campus. Which two precautions should IT take to prevent WannaCry ransomware from spreading to all clients? (Choose two.)

A.

Segment different departments to different IP blocks and enable Dynamic ARp inspection on all VLANs

B.

Ensure that noncompliant endpoints are segmented off to contain any potential damage.

C.

Ensure that a user cannot enter the network of another department.

D.

Perform a posture check to allow only network access to (hose Windows devices that are already patched.

E.

Put all company users in the trusted segment of NGFW and put all servers to the DMZ segment of the Cisco NGFW. ni

Full Access
Question # 124

Which CLI command is used to enable URL filtering support for shortened URLs on the Cisco Secure Email Gateway?

A.

outbreakconfig

B.

websecurityconfig

C.

webadvancedconfig

D.

websecurityadvancedconfig

Full Access
Question # 125

Which security principle advocates rapid cryptographic algorithm replacement to defend against quantum-computing threats?

A.

Crypto agility

B.

Zero trust

C.

Network slicing

D.

Key escrow

Full Access
Question # 126

Which feature is used to restrict communication between interfaces on a Cisco ASA?

A.

VLAN subinterfaces

B.

Traffic zones

C.

Security levels

D.

VxLAN interfaces

Full Access
Question # 127

Which two cryptographic algorithms are used with IPsec? (Choose two)

A.

AES-BAC

B.

AES-ABC

C.

HMAC-SHA1/SHA2

D.

Triple AMC-CBC

E.

AES-CBC

Full Access
Question # 128

Refer to the exhibit.

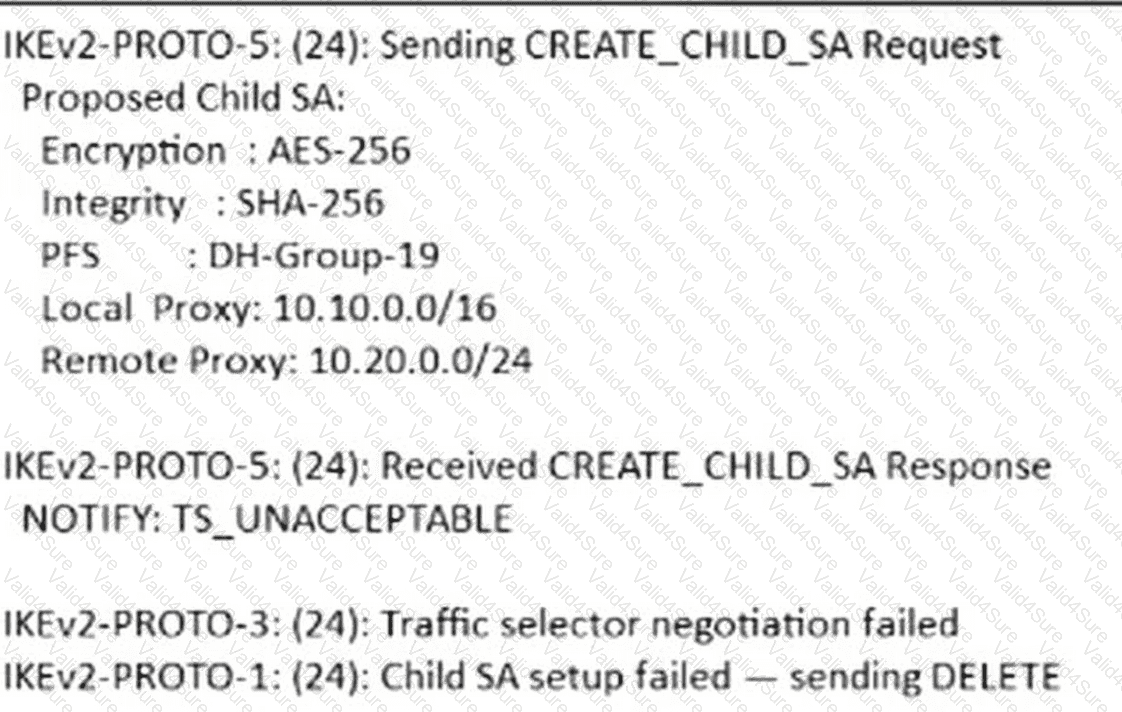
A site-to-site IKEv2 VPN between two Cisco Secure Firewall Threat Defense devices at a healthcare organization completes IKE Phase 1 successfully but fails during CREATE_CHILD_SA. The engineer captures the debug output from the initiating Cisco Secure Firewall. Which action must be performed to resolve the issue?

A.

Align the protected network definitions on both firewalls so that the local and remote traffic selectors proposed during CREATE_CHILD_SA match on both peers.

B.

Change the IPsec encryption algorithm from AES-256 to AES-128 on the initiating firewall and redeploy the VPN policy.

C.

Extend the IKE SA lifetime on both firewalls to give CREATE_CHILD_SA sufficient time to complete the negotiation before the Phase 1 SA expires.

D.

Remove DH Group 19 from the IPsec proposal on the initiating FTD because the TS_UNACCEPTABLE notification indicates that the responder does not support the proposed PFS group.

Full Access
Go to page: