Special Month End Sale - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 75vsure

300-710 Exam Dumps - Securing Networks with Cisco Firepower (300-710 SNCF) v1.2

Searching for workable clues to ace the Cisco 300-710 Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s 300-710 PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps

Go to page:
Question # 113

An engainermust add DNS-specific rules to me Cisco FTD intrusion policy. The engineer wants to use the rules currently in the Cisco FTD Snort database that are not already enabled but does not want to enable more than are needed. Which action meets these requirements?

A.

Change the dynamic state of the rule within the policy.

B.

Change the base policy to Security over Connectivity.

C.

Change the rule state within the policy being used.

D.

Change the rules using the Generate and Use Recommendations feature.

Full Access
Question # 114

What is a characteristic of bridge groups on a Cisco FTD?

A.

In routed firewall mode, routing between bridge groups must pass through a routed interface.

B.

In routed firewall mode, routing between bridge groups is supported.

C.

In transparent firewall mode, routing between bridge groups is supported

D.

Routing between bridge groups is achieved only with a router-on-a-stick configuration on a connected router

Full Access
Question # 115

A network administrator notices that SI events are not being updated The Cisco FTD device is unable to load all of the SI event entries and traffic is not being blocked as expected. What must be done to correct this issue?

A.

Restart the affected devices in order to reset the configurations

B.

Manually update the SI event entries to that the appropriate traffic is blocked

C.

Replace the affected devices with devices that provide more memory

D.

Redeploy configurations to affected devices so that additional memory is allocated to the SI module

Full Access
Question # 116

What must be implemented on Cisco Firepower to allow multiple logical devices on a single physical device to have access to external hosts?

A.

Add at least two container instances from the same module.

B.

Set up a cluster control link between all logical devices

C.

Add one shared management interface on all logical devices.

D.

Define VLAN subinterfaces for each logical device.

Full Access
Question # 117

A Cisco FTD has two physical interfaces assigned to a BVI. Each interface is connected to a different VLAN on the same switch. Which firewall mode is the Cisco FTD set up to support?

A.

active/active failover

B.

transparent

C.

routed

D.

high availability clustering

Full Access
Question # 118

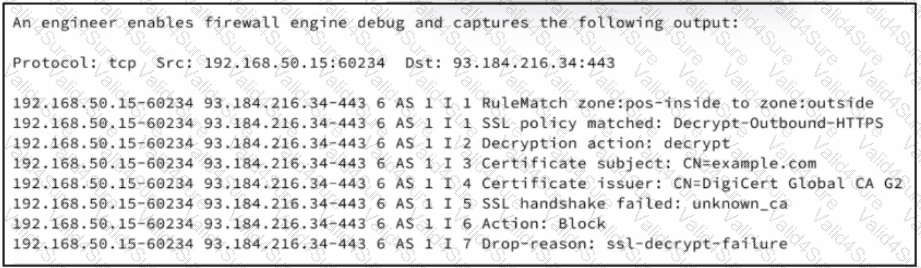
Refer to the exhibit.

Security engineer is investigating an issue where outbound HTTPS traffic from an endpoint using network 192.168.50.0/24 is being blocked. The Cisco Secure Firewall Threat Defense is configured with a TLS decryption policy applied to all outbound web traffic. An engineer enables firewall engine debug and captures the output. Which action must be performed to resolve the issue?

A.

Export the TLS re-signing CA certificate used by the SSL policy and deploy it to the trusted root store on the POS terminals.

B.

Enroll the FTD re-signing CA from the corporate internal CA and redeploy the SSL policy, trusted in the Windows certificate store.

C.

Add DigiCert Global CA G2 to the trusted CA list in the SSL policy to accept the external issuer during re-signing and complete the handshake.

D.

Add the destination IP range of POS terminal traffic to a URL-category-based SSL rule with the action set to Do Not Decrypt.

Full Access
Question # 119

A security engineer is deploying a pair of primary and secondary Cisco FMC devices. The secondary must also receive updates from Cisco Talos. Which action achieves this goal?

A.

Force failover for the secondary Cisco FMC to synchronize the rule updates from the primary.

B.

Configure the secondary Cisco FMC so that it receives updates from Cisco Talos.

C.

Manually import rule updates onto the secondary Cisco FMC device.

D.

Configure the primary Cisco FMC so that the rules are updated.

Full Access
Question # 120

An engineer configures an access control rule that deploys file policy configurations to security zones or tunnel zones, and it causes the device to restart. What is the reason for the restart?

A.

Source or destination security zones in the access control rule matches the security zones that are associated with interfaces on the target devices.

B.

The source tunnel zone in the rule does not match a tunnel zone that is assigned to a tunnel rule in the destination policy.

C.

Source or destination security zones in the source tunnel zone do not match the security zones that are associated with interfaces on the target devices.

D.

The source tunnel zone in the rule does not match a tunnel zone that is assigned to a tunnel rule in the source policy.

Full Access
Go to page: