
Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: scxmas70

SPLK-5002 Exam Dumps - Splunk Certified Cybersecurity Defense Engineer

Searching for workable clues to ace the Splunk SPLK-5002 Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s SPLK-5002 PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps

Go to page:
Question # 9

Based on the provided screenshot, different machines or accounts have been associated with chosen threat objects. Which two Enterprise Security frameworks are responsible for programmatically associating this information?

A.

Threat Intelligence, Risk

B.

Risk, Assets & Identities

C.

Risk, Incident Review

D.

Threat Intelligence, Assets & Identities

Full Access
Question # 10

For detections that leverage a CIM data model, which aspect of the configuration is responsible for determining which indexes are being searched?

A.

The data model ' s constraint macro.

B.

The data model ' s index list.

C.

The data model ' s root expression.

D.

The data model ' s dataset hierarchy.

Full Access
Question # 11

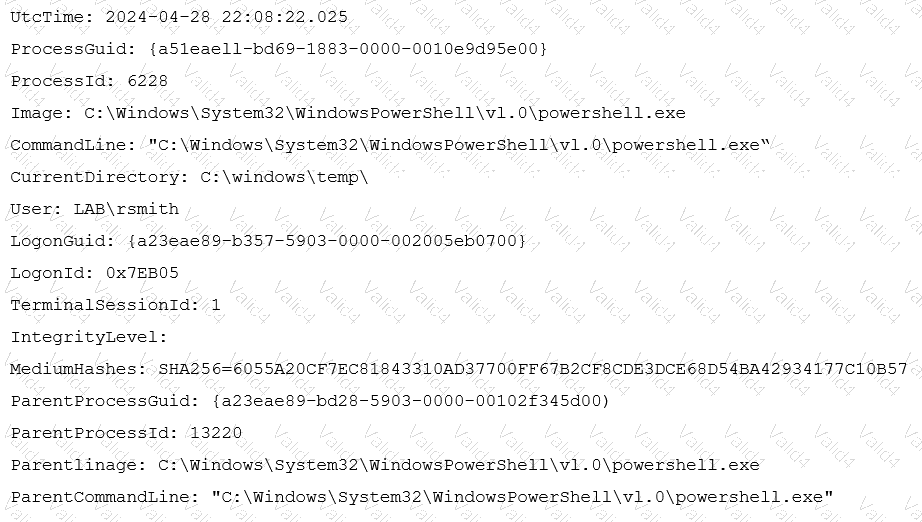
Below is an example of a Sysmon process create log. Which EventCode would be associated with this log entry?
A.

EventCode=1

B.

EventCode=4

C.

EventCode=3

D.

EventCode=2

Full Access
Question # 12

Which of the following should an engineer do as they evaluate their Threat Detection and Incident Response lifecycle?

A.

Focus efforts on the least impactful threat vectors.

B.

Use the MITRE ATT & CK Framework to evaluate the organization ' s risk appetite.

C.

Evaluate the threat process lifecycle solely from predefined technical profiles.

D.

Evaluate the threat process lifecycle based on contextual business and industry knowledge.

Full Access
Question # 13

Based on a recent red team exercise, an organization is highly concerned about pass the hash attacks especially including tools like Empire. Which EventCode associated to PowerShell Script Block Logging would be used to detect this activity?

A.

EventCode=4126

B.

EventCode=4168

C.

EventCode=4624

D.

EventCode=4104

Full Access
Question # 14

In Enterprise Security, what is the name of the threat intelligence lookup pertaining to files?

A.

file_hash

B.

file_intel

C.

user_intel

D.

user_hash

Full Access
Question # 15

A cyber defense engineer plays a role in maintaining a secure SOAR Cloud configuration. Which network security statement is correct about SOAR Cloud?

A.

Splunk Cloud initiates an outbound SSL connection to both the Automation Broker and managed endpoints.

B.

The Automation Broker initiates an outbound SSL connection to Splunk Cloud, and also initiates an outbound connection to the managed endpoints.

C.

The Automation Broker initiates an inbound SSL connection to Splunk Cloud, and also initiates an outbound connection to the managed endpoints.

D.

The Automation Broker initiates an outbound SSL connection to Splunk Cloud, and the managed endpoint initiates an outbound connection to the Automation Broker.

Full Access
Question # 16

What is a key feature of effective security reports for stakeholders?

A.

High-level summaries with actionable insights

B.

Detailed event logs for every incident

C.

Exclusively technical details for IT teams

D.

Excluding compliance-related metrics

Full Access
Go to page: