Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: scxmas70

JN0-336 Exam Dumps - Security, Specialist (JNCIS-SEC)

Searching for workable clues to ace the Juniper JN0-336 Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s JN0-336 PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps

Go to page:
Question # 9

You work on the security operations team that manages firewalls only. In your data center, there are two SRX chassis clusters. These clusters operate on VLAN 1042. The network team advises you that they see the same MAC address coming from both chassis clusters for reth0.

Why is this occurring?

A.

The same cluster ID was used on both clusters.

B.

RGO is active on both node0 and node1 due to split-brain.

C.

Chassis clusters must be on separate VLANs.

D.

Link Aggregation Control Protocol is not synchronized.

Full Access
Question # 10

Which two statements are correct about a chassis cluster? (Choose two.)

A.

If the cluster ID is set to 0, the HA configuration is ignored.

B.

You must reboot the device anytime you change the node ID configuration.

C.

If the node ID is set to 0, the HA configuration is ignored.

D.

You must have multiple Layer 2 domains if you require more than 255 node IDs.

Full Access
Question # 11

Which three different objects would be created, modified, cloned, and deleted in the Shared Objects workspace of Junos Space Security Director? (Choose three.)

A.

geo IP

B.

IP address

C.

audit logs

D.

policy enforcement groups

E.

policy rules

Full Access
Question # 12

You have configured a new site-to-site VPN tunnel. The exhibit shows the security IPsec statistics output for the specific tunnel index from one of the tunnel-end devices.
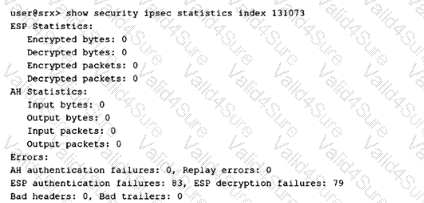
Which two statements are correct in this scenario? (Choose two.)

A.

AH is incorrectly configured.

B.

The far-end tunnel device is rebooting.

C.

The ESP configuration is not set up correctly.

D.

No traffic passes through this tunnel.

Full Access
Question # 13

You are establishing an IPsec VPN and must ensure that payload data is encrypted.

In this scenario, which IPsec security protocol should you configure?

A.

SHA-1

B.

ESP

C.

AH

D.

PFS

Full Access
Question # 14

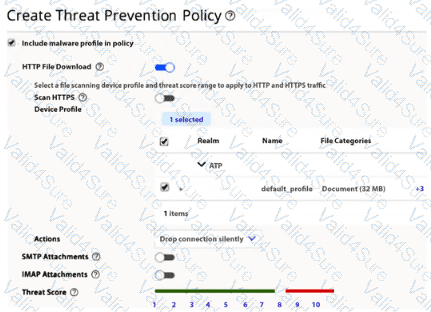
Referring to the exhibit, what should you do to ensure that Juniper ATP Cloud detects malware in HTTPS traffic?
A.

Manually configure and apply an SSL proxy profile.

B.

Lower the threat score.

C.

Configure a new device profile that includes encrypted traffic.

D.

Change the action to redirect the encrypted traffic to a decryption device.

Full Access
Question # 15

Which two statements are correct about Juniper ATP Cloud malware analysis? (Choose two.)

A.

If no match exists in cache, the remaining analysis features are processed with the cumulative threat score transmitted to the SRX Series device.

B.

If a match exists in cache, that threat score is sent to the SRX Series device and the analysis continues.

C.

If a match exists in cache, that threat score is sent to the SRX Series device and the analysis stops.

D.

If no match exists in cache, the first analysis feature to generate a threat score is transmitted to the SRX Series device.

Full Access
Question # 16

You are implementing an SRX Series device at a branch office that has low bandwidth and also uses a cloud-based VoIP solution with an outbound policy that permits all traffic.

Which service would you implement at your edge device to prioritize VoIP traffic in this scenario?

A.

AppFW

B.

SIP ALG

C.

AppQoE

D.

AppQoS

Full Access
Go to page: