GH-600 Exam Dumps - Developing in Agentic AI Systems
Searching for workable clues to ace the Microsoft GH-600 Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s GH-600 PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps
You need to make changes to repo1 to support the planned changes for the agents.
What should you modify?
You have a GitHub Enterprise repository that runs an autonomous agent by using a GitHub Actions workflow. The workflow has the following jobs:
agent-run that generates trace.json and plan.md
review that waits for human approval before continuing
deploy that uses the outputs from agent-run
You need to make the files inspectable in the GitHub Actions UI and ensure that the files are available to the review and deploy jobs.
What should you do in the workflow?
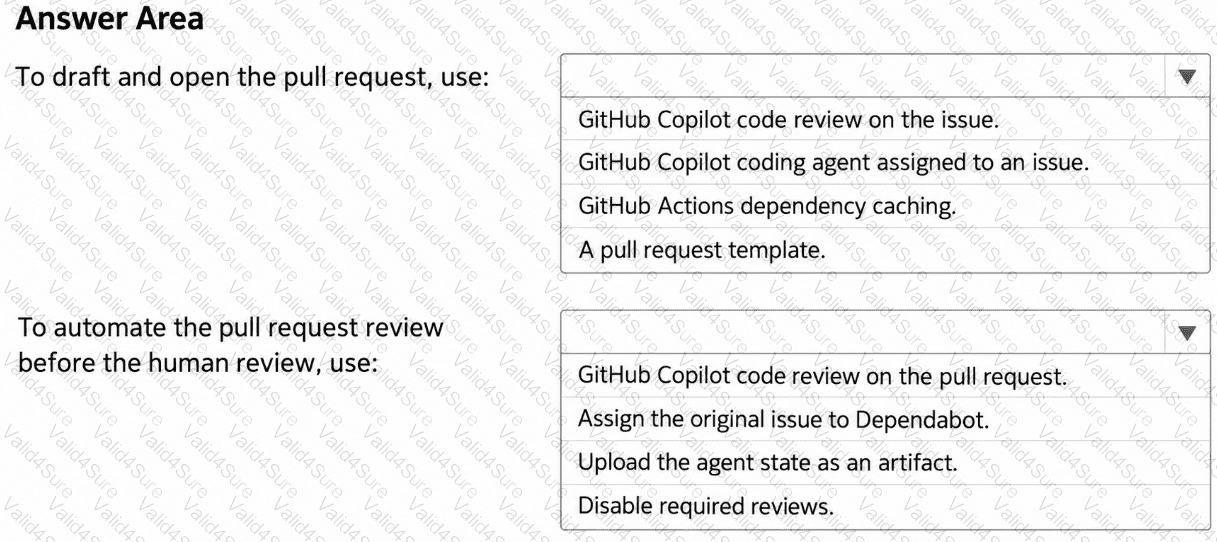
You have a GitHub Enterprise Cloud repository that uses GitHub Actions for CI and requires pull requests for all changes.
You are planning a GitHub Actions workflow where a coding agent drafts implementation changes and tests from GitHub issues, and an automated review runs before human review.
You need the agent to draft changes from an assigned issue, open a pull request, and add an automated review to the pull request before requesting a human review.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You use a GitHub Actions workflow to orchestrate a multi-agent draft-review process for pull requests. The workflow uploads a single combined review-package artifact at the end of each run.
You discover that the review-package artifact is occasionally missing from the workflow run history, and you suspect that a user deleted it.
You need to identify which user manually deleted a workflow run artifact and when the deletion occurred.
What should you use?
You have a GitHub Enterprise Cloud organization that uses the GitHub Copilot coding agent.
Copilot creates a draft pull request for an assigned issue, and the pull request timeline shows Copilot started work.
After 70 minutes, the agent session log stops updating, and the pull request body status stops changing.
You need to restart the agent so that it continues the task from the issue context and produces new commits to the existing draft pull request.
What should you do?
You have a GitHub Enterprise Cloud repository that uses the GitHub Copilot coding agent to implement changes by creating draft pull requests in a firewalled GitHub Actions environment.
Repository administrators add a Model Context Protocol (MCP) server configuration so that the agent can query an external system while it executes issues. The MCP server requires an API key, and the key must be provided to the MCP server as an environment variable when the server starts.
You create an environment secret named copilot_mcp_api_key that contains the API key.
You need to configure the repository to ensure that the MCP server receives the API key at runtime. The solution must ensure that only the intended secret is available to the MCP configuration.
What is the best option to use to achieve the goal?
You want to prevent GitHub Copilot from ever suggesting completions or making edits inside a directory containing sensitive credentials templates. What should you configure?
You need to resolve the scoping issue associated to agent1.
What should you do?