CY0-001 Exam Dumps - CompTIA SecAI+ v1 Exam
Searching for workable clues to ace the CompTIA CY0-001 Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s CY0-001 PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps
During an update, an AI system flags some potential compatibility issues and provides recommendations. An administrator reviews the recommendations before addressing the issues.
Which of the following processes describes this scenario?
An architect is using the firm ' s recommended large language model (LLM) to find an internal solution for content management.
Given the following:
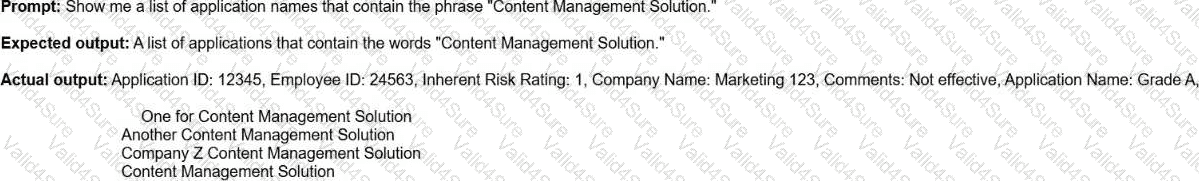
Which of the following controls is the best for mitigating this issue?
An AI security architect needs to conduct a security review of a new AI chatbot. Which of the following resources would the architect most likely rely on to perform a threat assessment and ensure comprehensive coverage during the review?
A loan company compares a machine learning model that was found on the dark web with the company ' s proprietary model. Using proprietary information, the company generates the following:
Input
Dark web model
Company ' s proprietary model
Jane A.
Approve
Approve
John B.
Deny
Deny
Ann J.
Deny
Deny
Joe H.
Approve
Approve
Which of the following should the AI red team recommend to mitigate risks for future deployments?
Which of the following best describes the risk of too many epochs on the same data?
An architect is creating a threat model for an agentic system.
Which of the following should the architect do first?
Which of the following improves the observability and auditing of an AI system?
A cybersecurity engineer implements a large language model (LLM) tool to automate an incident management workflow. However, the output contains items that do not exist in the real world. Which of the following is a technique to address this issue?